What Is MCP (Model Context Protocol)? A Guide for Data Teams
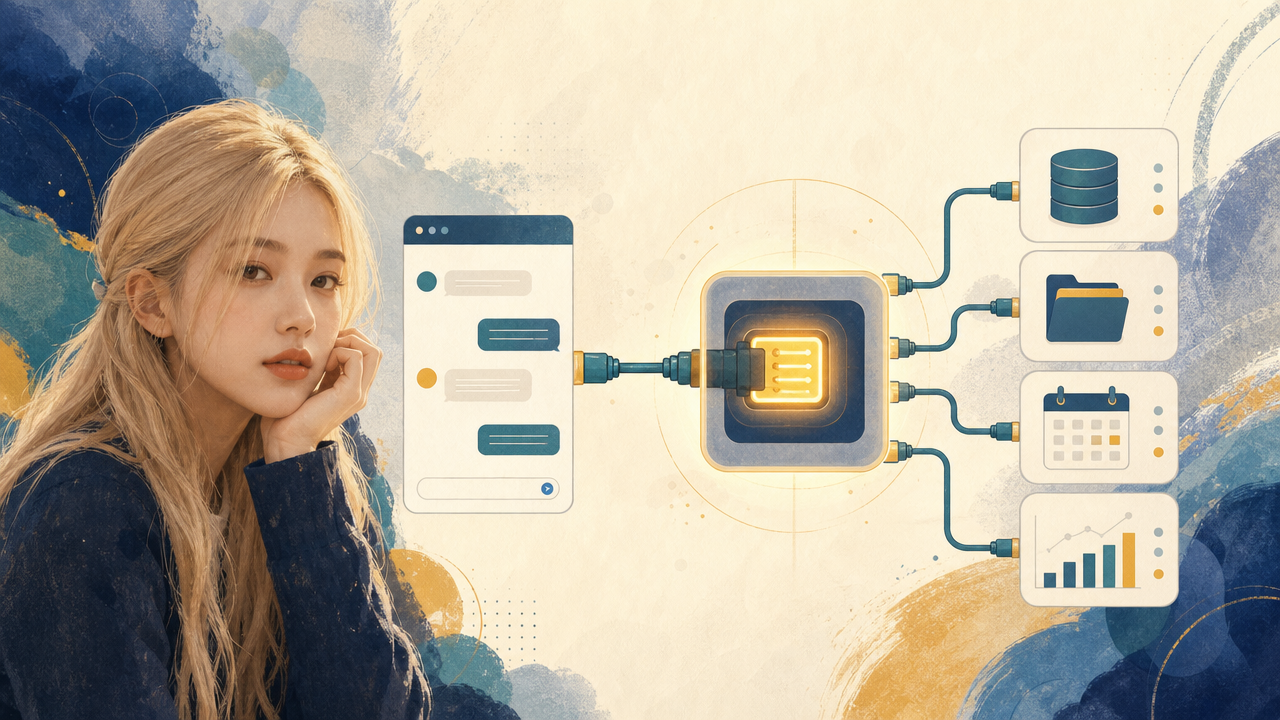
MCP (Model Context Protocol) is an open standard for connecting AI applications (like Claude, ChatGPT or an AI-enabled code editor) to external data and tools, such as databases, file systems, business apps and APIs. Instead of building a custom integration for every pair of AI app and tool, a tool is wrapped once as an MCP server, and any MCP-compatible AI application can use it. Its own documentation compares it to a USB-C port for AI.
For data teams, MCP is the piece that lets an AI assistant query your warehouse, read your dbt project or check a dashboard's definitions, instead of guessing from whatever you paste into the chat. It's also becoming core infrastructure for AI agents, so it's worth understanding even if you never build a server yourself.
The Problem MCP Solves
Before MCP, every connection was custom. If you had 5 AI applications and wanted each to reach 10 data sources, you potentially needed 50 separate integrations, each with its own authentication, formats and maintenance.
MCP turns that into a "build once, use everywhere" problem. Each data source gets one MCP server, and each AI application implements MCP once. Five apps and ten sources then need 15 components instead of 50 integrations. That's why a standard can take off quickly: every new server is immediately useful to every compatible app.
A Short History
November 2024: Anthropic released MCP as an open-source specification.
2025: it was adopted well beyond Anthropic. OpenAI, Google, Microsoft and major developer tools added support.
December 2025: Anthropic donated MCP to the newly formed Agentic AI Foundation, a fund under the Linux Foundation co-founded by Anthropic, Block and OpenAI. That gave the protocol neutral governance.
2026: the specification keeps evolving through dated revisions (the current one at the time of writing is 2026-07-28), and many AI assistants and code editors support it.
How MCP Works: Hosts, Clients and Servers
MCP has three participants:
Participant
What it is
Example
Host
The AI application the user works in
Claude Desktop, ChatGPT, VS Code, Cursor
Client
A connector inside the host. There's one client per server connection
Created automatically by the host
Server
A program that exposes data and actions to the AI
A PostgreSQL server, a GitHub server, your company's internal metrics server
Servers can run locally on your machine (communicating over standard input/output) or remotely over the web (using a transport called Streamable HTTP, with OAuth recommended for authentication). Messages use a simple, widely used format called JSON-RPC.
What a Server Can Offer: Tools, Resources and Prompts
MCP servers expose three main kinds of things:
Tools:actions the AI can call, like "run this SQL query", "create a ticket" or "refresh this dataset". Each tool has a name, a description and a defined input format, so the model knows when and how to use it.
Resources:data the AI can read for context, like a table's schema, a file or a metric definitions document.
Prompts: reusable templates the server provides, such as "analyze week-over-week change for metric X".
In the other direction, a server can ask the user for more input or confirmation through the host (called elicitation), for example "this query will scan 2 TB, proceed?".
A Data Team Example
A company sets up a read-only warehouse MCP server that exposes:
A resource with the schema of the approved analytics tables (fact_sales, dim_store, dim_date)
A resource with the official metric definitions ("net revenue = gross sales − refunds − discounts")
A toolrun_readonly_query(sql) that runs SQL with a row limit and a timeout
An analyst asks the assistant: "Which regions missed their Q3 net revenue target, and by how much?"
The host has already discovered the server's tools and resources.
The model reads the schema and the metric definitions, so it uses the official net revenue formula, not its own guess.
It calls run_readonly_query with a SQL query joining sales to targets.
The server runs the query under the analyst's permissions and returns the rows.
The model summarizes the answer, and the analyst can inspect the exact SQL that ran.
Compared with pasting a CSV into a chat, the data is current, the definitions are consistent, and the query can be checked afterwards. Grounding answers in trusted sources is the same idea behind RAG, applied to live systems and actions instead of documents.
MCP vs Function Calling vs RAG vs Agent Frameworks
What it is
Relationship to MCP
Function / tool calling
A model's ability to output a structured request to call a tool
MCP standardizes how tools are described and connected, and function calling is how the model asks to use them
RAG
Retrieving relevant documents to ground an answer
A retrieval system can be exposed through an MCP server
Agent frameworks (LangGraph, CrewAI, AutoGen)
Libraries for orchestrating multi-step agent logic
Connecting AI to real systems creates real risks. The main ones:
Excessive permissions. A server with write access to production data lets a confused or manipulated model do real damage. Start read-only, limit scope, and use the user's own permissions rather than a powerful shared account.
Prompt injection through data. Text returned by a tool (a web page, a support ticket, even a database field) can contain instructions aimed at the model. Treat all tool output as untrusted data, and require human confirmation for consequential actions.
Untrusted servers. Installing a random MCP server is like installing any software. It runs with whatever access you give it. Use official or reviewed servers, and pin versions.
Data leakage. Anything a tool returns goes into the model's context. Mask sensitive columns at the server, and remember that large results also cost tokens (why that matters).
Cost and runaway queries. Add row limits, timeouts and query cost caps on warehouse tools.
These are the same failure modes we cover in Why Most AI Agents Fail in Production. Most real incidents come from permissions and missing guardrails, not from the protocol itself.
Should You Learn MCP?
Analysts and business users: understand the concepts so you can use MCP-connected assistants well and ask your data team for the right connectors. You don't need to build servers.
Data and analytics engineers: learning to build a simple, secure, read-only server for your warehouse or semantic layer is becoming a practical, valued skill. Official SDKs exist for Python, TypeScript and several other languages.
AI engineers: MCP is now part of the standard toolkit for building agents, alongside an agent framework and evaluation practices.
Is MCP only for Claude?
No. Anthropic created it, but it's an open standard now governed under the Linux Foundation's Agentic AI Foundation, and it's supported by ChatGPT, major code editors and many other AI tools.
Is MCP the same as an API?
No. MCP is a standard way of wrapping APIs and data sources for AI applications. An MCP server usually calls ordinary APIs or databases behind the scenes, and adds descriptions that let a model discover and use them.
Do I need to code to use MCP?
Not to use it. Many AI apps let you add existing servers through settings. Building your own server requires programming, typically in Python or TypeScript with an official SDK.
Is MCP secure?
The protocol supports standard authentication such as OAuth, but safety depends mostly on how servers are built and configured: least-privilege access, read-only defaults, confirmation for risky actions, and trusted sources only.
Bottom Line
MCP is the open standard that lets AI applications connect to data and tools through reusable servers, which expose tools, resources and prompts to any compatible host. For data teams, it means AI assistants that work with your live warehouse and official metric definitions instead of pasted CSVs. The value is real, and so are the risks, so start read-only, keep permissions narrow, and treat everything a tool returns as untrusted input.